Endpoint Program Gaps Most Commonly Found in SMB Security Audits
Small teams struggle to keep their endpoint protections working as deployed.
Yolanda Ferreira-Boateng
Small teams struggle to keep their endpoint protections working as deployed.
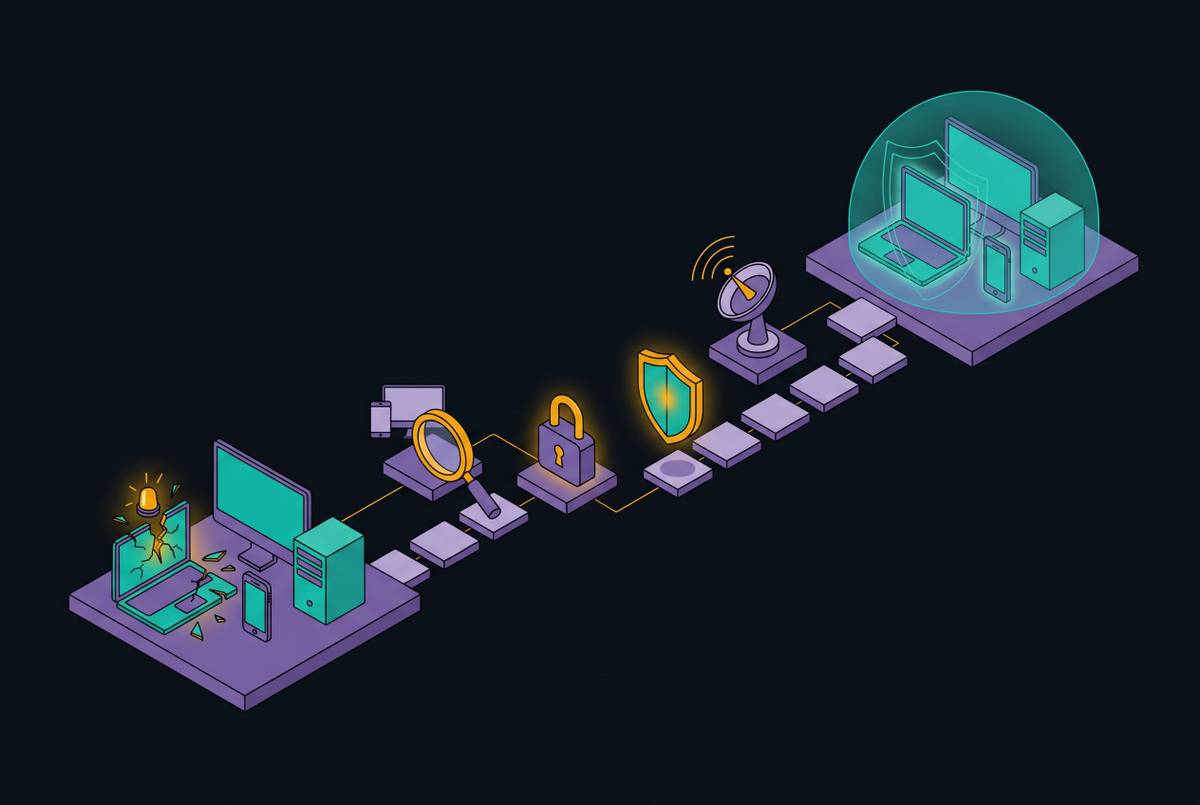
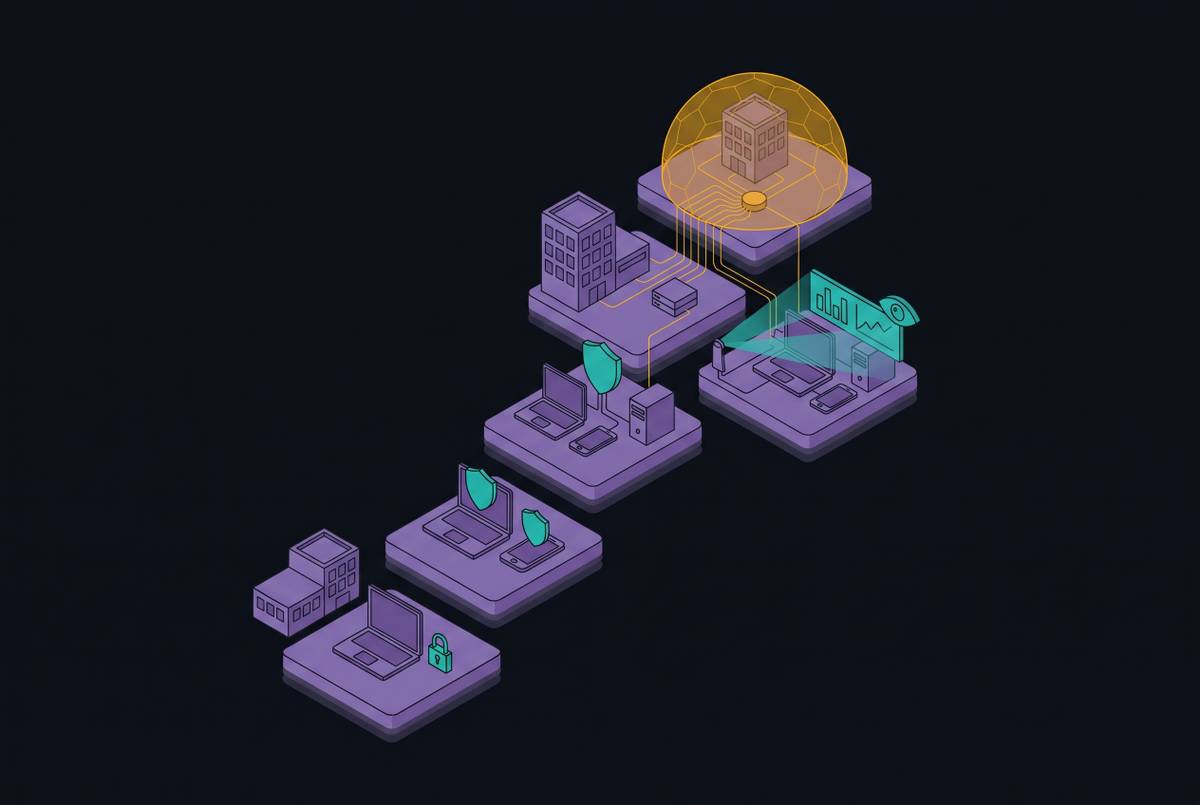
SMBs need a phased 90-day plan to close gaps and assign owners, not a comprehensive overhaul.
A phased approach helps lean teams close security gaps without building unsustainable programs.
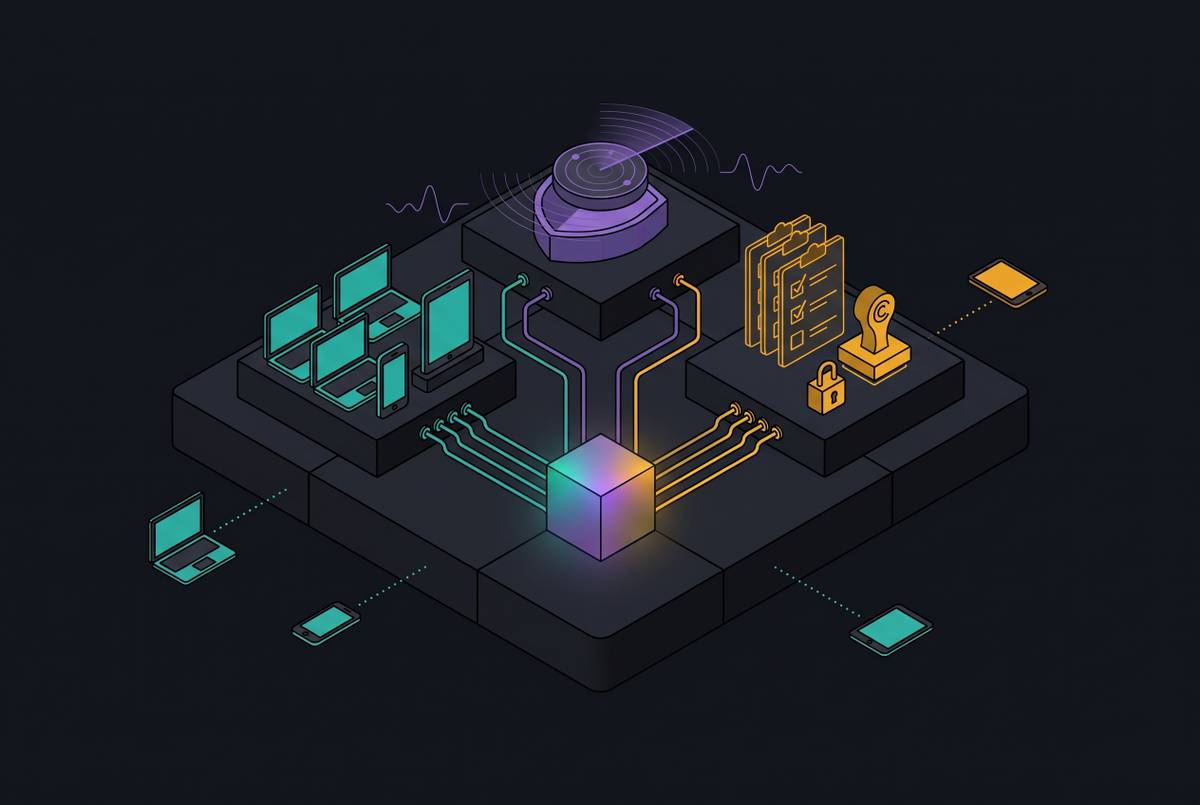
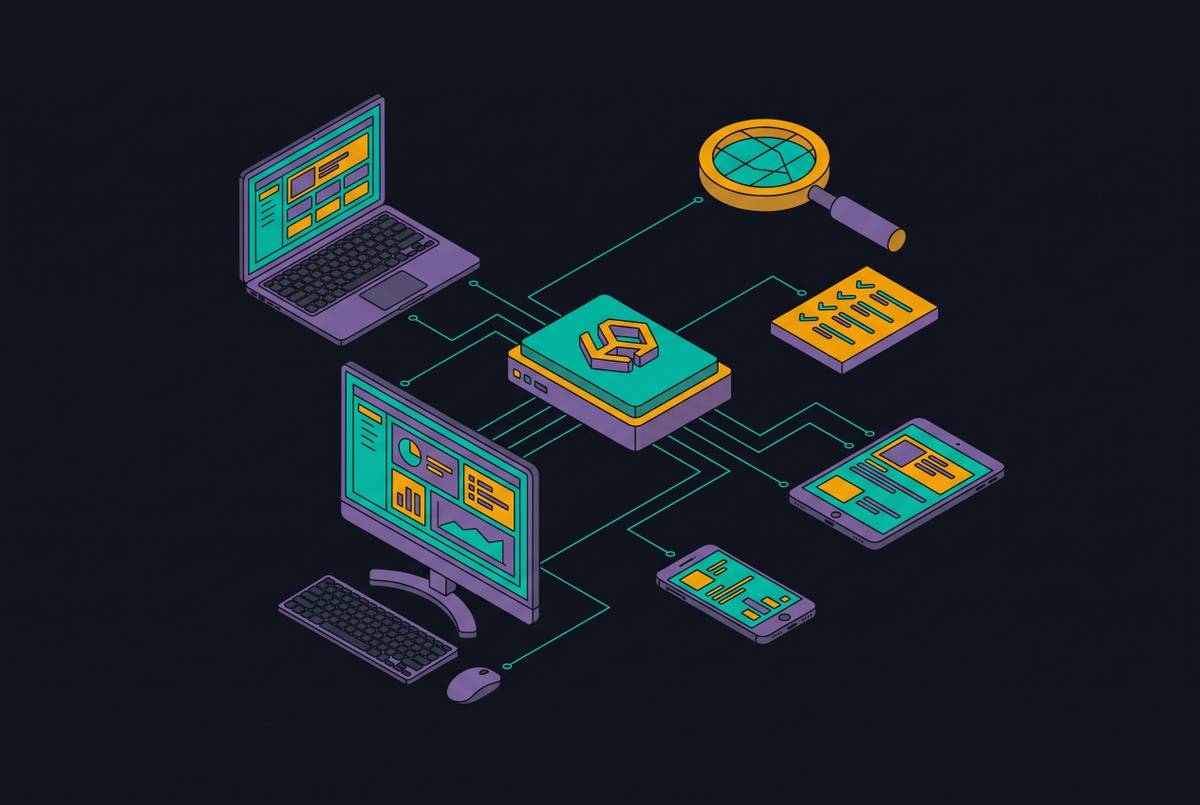
One integrated platform beats three consoles for small teams without security staff.
Separate MDM and EDR tools leave a dangerous gap only someone can own.
Integrate compliance evidence collection into endpoint management to build continuous audit trails.
Security leaders should measure endpoint protection by business risk, not technical workload.
Unified platforms eliminate handoffs and gaps that slow threat response and audit preparation.
Staffless businesses should prioritize deployment speed and managed response over technical specs.
Small businesses need automation to enforce security controls nobody has time to manage.
Small companies need managed EDR with overnight staffing to actually use endpoint alerts.
Unpatched browser sessions expose SaaS data that endpoint defenses cannot see.